Tuesday, 10 November 2026
European data protection regulators are reporting increased numbers of security incidents and complaints as businesses face closer examination of how they collect, manage and protect personal information. Developments highlighted in the November 2026 data protection review by international law firm CMS include changes to regulatory guidance, concerns surrounding artificial intelligence and enforcement action involving major technology businesses.
Germany has seen particularly notable increases in reported incidents. In Rhineland-Palatinate, authorities recorded 1,796 data protection complaints and 1,101 reported breaches during the first nine months of 2026, already exceeding the totals for the whole of 2025. Berlin has also reported that its 2026 figures have surpassed the previous year’s level.
Lower Saxony’s data protection authority reported a 58% increase in notified incidents by the end of the third quarter. Regulators have highlighted the importance of measures such as multifactor authentication, employee training and more consistent internal procedures for identifying and responding to security breaches. Some authorities have also raised concerns about the growing use of artificial intelligence in activities involving personal data.
At European level, the European Data Protection Board has continued work on guidance intended to improve consistency in the application of data protection legislation. Recent developments include a methodology for assessing financial penalties and guidance addressing the relationship between the General Data Protection Regulation and the Digital Services Act. These initiatives are intended to clarify how regulators assess compliance and apply overlapping legal requirements.
The European Data Protection Supervisor has also published additional guidance concerning the reporting of personal data breaches. Its recommendations address the assessment of potential harm, notification procedures and steps to reduce the consequences of security incidents. The guidance provides a reference point for organisations reviewing their internal response arrangements, although the Supervisor’s direct regulatory responsibilities differ from those of national authorities overseeing private businesses.
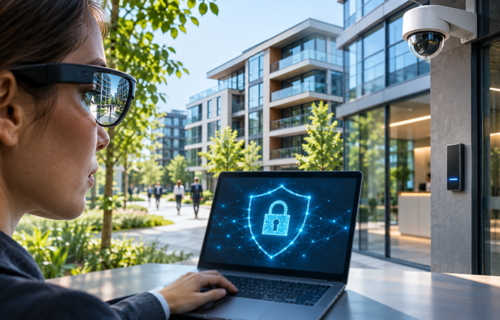
New technologies are creating further questions about privacy protection. In Germany, Hamburg’s data protection authority has examined smart glasses equipped with cameras, microphones and artificial intelligence capabilities. The review identified concerns about recording individuals without their knowledge and the difficulties of establishing an appropriate legal basis for processing the information collected.
The European Data Protection Board has separately addressed privacy risks associated with smart glasses, reflecting growing regulatory attention to devices capable of collecting information in public and commercial environments. Such technologies may also become relevant to workplaces, retail premises and other managed properties where recording equipment interacts with visitors and employees.
CMS also reported significant enforcement decisions involving technology platforms and healthcare information. The cases illustrate the potential consequences of processing personal information without an adequate legal basis or appropriate safeguards. However, individual penalty amounts and the procedural status of the decisions require confirmation from the issuing authorities before being treated as established enforcement outcomes.
For the real estate industry, data protection requirements extend beyond traditional information technology operations. Property owners and managers routinely handle tenant records, access-control information, visitor registrations, surveillance footage and employee data. As buildings incorporate more connected systems and digital services, the governance of personal information is becoming an increasingly important operational consideration.
The developments suggest that businesses should assess not only their cybersecurity arrangements but also the purposes for which information is collected, who can access it and how incidents are managed. The latest regulatory activity does not create a single new compliance requirement for the property sector, but it reinforces the need to account for data protection when introducing digital building technologies and managing information across property portfolios.
Source: CMS Data Protection Update, November 2026